
Employee Security Training
Your team is the firewall. Train it like one.
Technology stops most attacks, but people decide the rest. One phishing email bypasses every filter if an employee clicks. AllGuard IT trains your Maryland, Washington DC, and Virginia team to spot phishing, handle passwords properly, and pause before clicking, using short, plain-language sessions and simulated phishing tests that show whether the training is working. That covers phishing simulations, short training sessions, and password habits your team can actually keep.
What’s Included
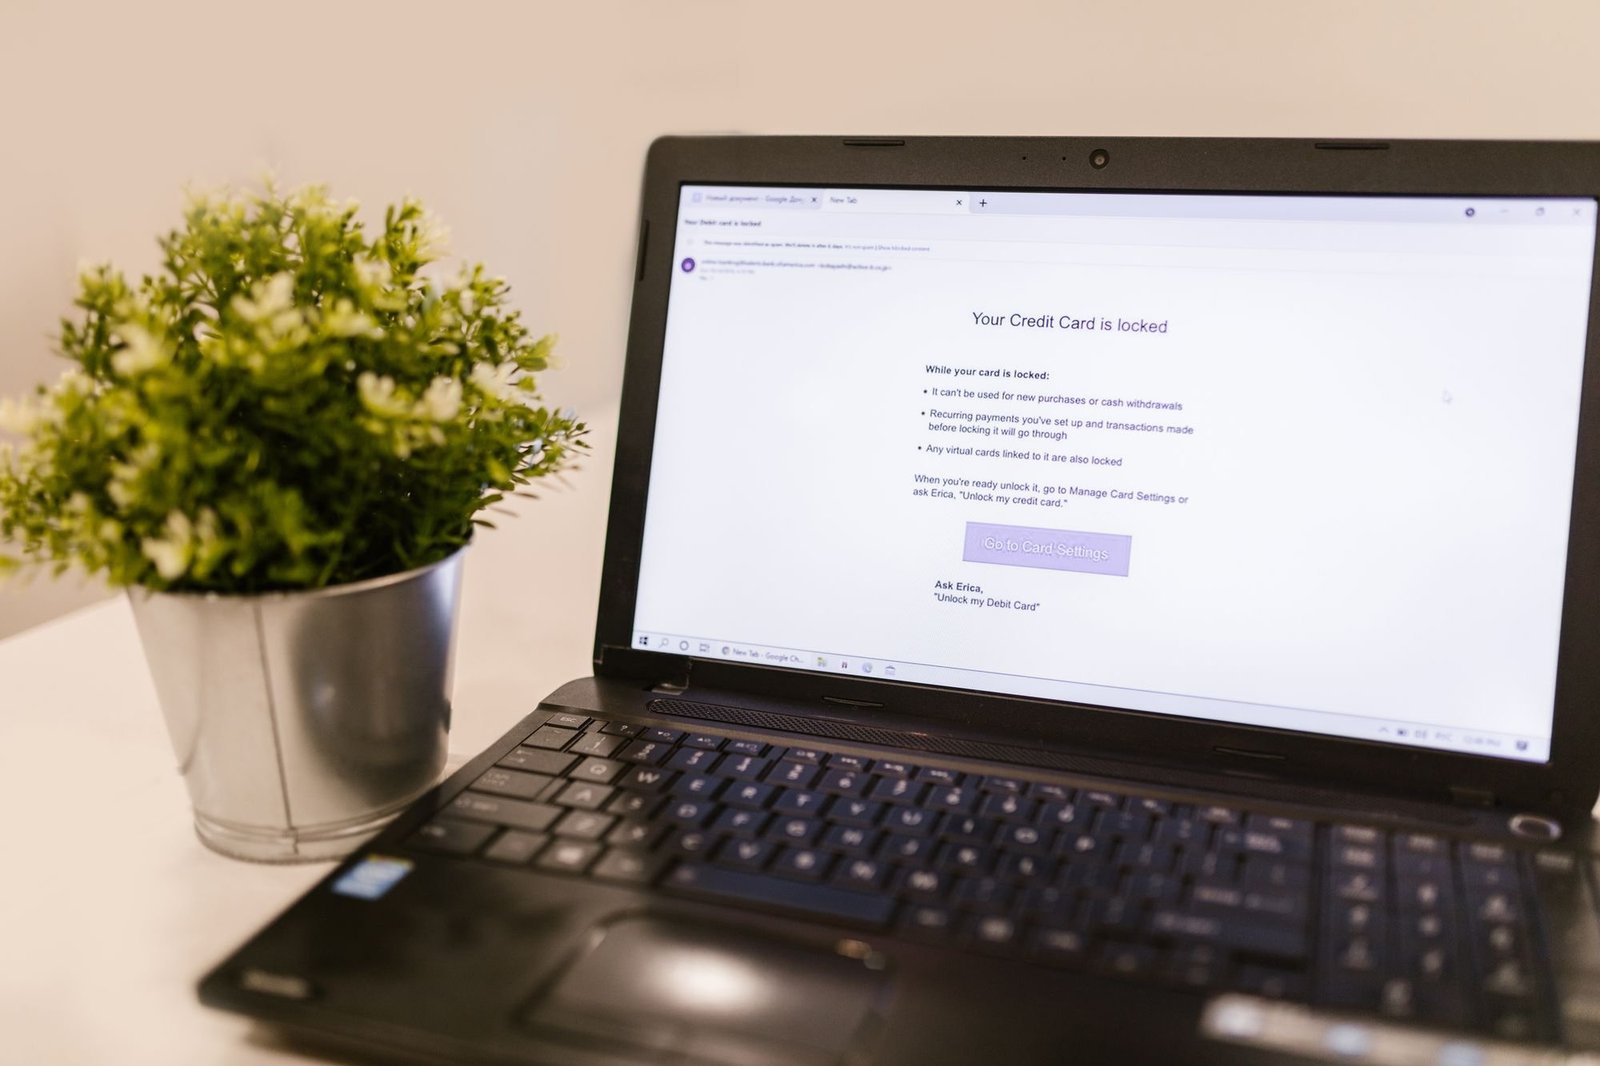
Phishing Simulations
We send safe, realistic fake phishing emails to your team: the same styles attackers use, from fake invoices to password resets. Clicks are tracked privately, and the results show exactly where extra coaching will help most.

Training Sessions
Short sessions in plain language: no jargon, no fear tactics, no hour-long lectures. We use real examples your team will recognize, explain what attackers are counting on, and keep it practical enough that people remember it on a busy Tuesday.

Password Practices
Most password rules fail because nobody can follow them. We teach realistic habits your team will actually use: long passphrases, a password manager where it fits, and multi-factor authentication, instead of sticky-note passwords changed every 30 days.

New-Hire Onboarding
New employees are prime phishing targets, because they don’t know your normal processes yet. Security basics are built into onboarding, so every new hire learns how your business handles passwords, payments, and suspicious messages from their first week.
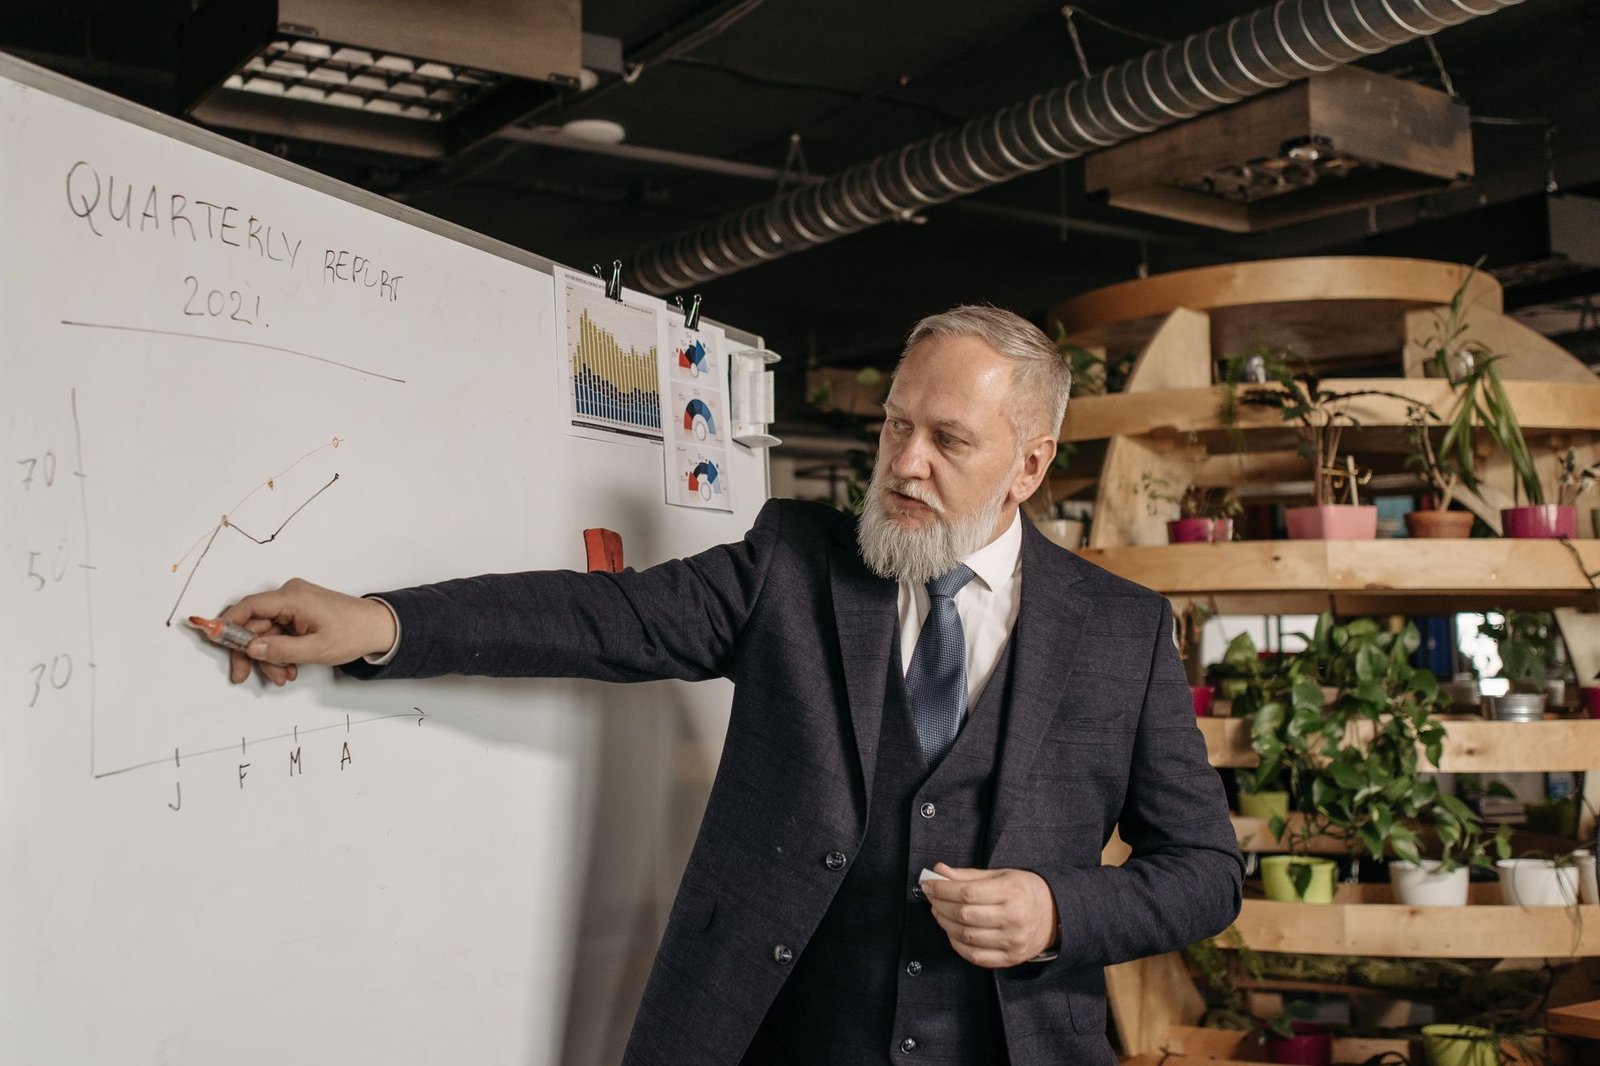
Progress Reporting
You receive progress reporting that shows trends: who’s improving, which topics still trip people up, and where follow-up coaching is needed. We report patterns to management, not names, so training stays supportive instead of becoming a blame exercise.
How It Works
Baseline
We start with a first simulated phishing round. No one is in trouble. It simply shows where your team stands today, so training targets real weaknesses.
Train
Sessions are built around the weaknesses the baseline exposed. If invoice scams fooled people, that’s what we practice, in short sessions that fit a working day.
Retest
Ongoing simulations and refreshers prove the training sticks, because one annual session fades fast, while regular practice keeps spotting phishing a habit, not a memory.
Who It’s For
Any Maryland, Washington DC, and Virginia office whose team uses email, which means essentially everyone, and especially regulated industries like healthcare and finance, where a single click can put client and patient data at risk. It suits offices of any size, from a handful of staff to larger teams with new hires joining regularly.
Common Questions
Done right, it’s eye-opening, not embarrassing. We frame simulations as practice, not punishment, the same way a fire drill isn’t about catching people who run. Most staff actually get competitive about spotting the fakes, and the person who clicks learns the lesson in the one place it’s safe to learn it: a test, instead of a real attack on a Friday afternoon.
Ongoing beats annual. One long training video once a year is forgotten by February. Short sessions plus regular phishing simulations keep the habits fresh without eating the workday, a few minutes at a time, all year. (Security awareness training is already included in our Business plan, so for many clients there’s nothing extra to schedule or buy.)
It covers the security-awareness component most frameworks, including HIPAA, require, and we document it: who was trained, when, and how the simulations went. If an auditor or an insurance application asks for proof your team is trained, you’ll have it in writing instead of a shrug.
Extra coaching, not shame. Some people need the lesson explained a different way, and a few roles (anyone who handles payments or client data) may need tighter email rules around them while they learn. We report trends to management, not a wall of names: the goal is a team that gets harder to fool, not a person who gets punished.
Find out what your IT is really costing you.
A free 45-minute IT Check covering your systems, security gaps, and spend, explained in plain language. Keep the report either way.
Get my Free IT Check →